Board Governance, Conduct & Digital Resilience for Cyprus Investment Firms [SP0308]
A practical 4 CPD self-paced Board governance course for Cyprus Investment Firms (CIFs) covering corporate governance, CySEC regulatory oversight, risk appetite, financial resilience, MiFID II customer outcomes, AML/CFT, sanctions and digital operational resilience under DORA.
✓ Strengthen Board accountability, independent challenge and evidence-based governance decisions. ✓ Assess business growth, risk appetite, capital adequacy, liquidity and client protection from a Board perspective. ✓ Improve Board oversight of AML/CFT, sanctions, client assets, ICT incidents, DORA compliance and critical third-party risks. ✓ Apply regulatory governance principles through interactive Board scenarios, management information, case studies and a final assessment.The programme aims to equip participants with the knowledge, practical skills and professional judgement required to handle personal data responsibly, apply GDPR principles in everyday business activities, recognise data protection risks, and support effective organisational compliance through appropriate documentation, security measures and escalation procedures.
Table of Contents
- About the Course
- Why Take This Board Governance Course?
- Key Learning Objectives
- Course Curriculum
- Meet the Trainer
- FAQs – Frequently Asked Questions
- Fees & Registration Details
About the Course
Board Governance, Conduct & Digital Resilience for Cyprus Investment Firms is a practical online training programme designed for directors, non-executive directors, Board committee members and senior management of Cyprus Investment Firms (CIFs).
The course focuses on the responsibilities of the management body in overseeing corporate governance, business strategy, risk management, customer protection, financial crime and digital operational resilience within the Cyprus financial-services regulatory environment.
Effective governance requires more than approved policies and periodic reporting. Boards must understand the firm’s business model, challenge management assumptions, identify emerging risks, assess the quality of management information and demonstrate effective oversight through documented decisions and follow-up actions.
This self-paced Board governance training examines how directors can exercise meaningful oversight across interconnected regulatory and operational areas, including:
- Corporate Governance & CySEC Oversight: Board accountability, delegated responsibilities, governance structures, independent control functions and evidence-based decision-making.
- Risk Appetite & Business Strategy: Business-model sustainability, revenue concentration, risk limits, growth proposals and escalation.
- Financial Resilience: Capital and liquidity monitoring, stress testing and wind-down preparedness.
- MiFID II Conduct & Client Protection: Product governance, target markets, digital distribution, client outcomes, complaints and safeguarding.
- AML/CFT & Sanctions Governance: Board oversight of money laundering, terrorist financing, sanctions exposure, fraud and market-integrity risks.
- DORA & ICT Risk Management: Management-body accountability for ICT risk, operational disruptions, recovery and resilience.
- Outsourcing & Third-Party Risk: Critical ICT provider dependencies, subcontracting, concentration risk and exit planning.
Rather than focusing on operational compliance procedures, the programme examines what directors should approve, which management information they should expect, when they should challenge or escalate issues, and how governance decisions should be documented.
Participants work through realistic Board-level situations using a fictional digital retail Cyprus Investment Firm, including management dashboards, risk indicators, incomplete reporting and challenging decision scenarios.
The learning principles are designed to be applied proportionately to each firm’s regulatory permissions, business model, prudential classification, investment services, client-asset arrangements and third-party dependencies.
With 4 CPD credits and six months of online access, the programme offers a flexible way for experienced financial-services professionals to strengthen their Board governance and regulatory oversight capabilities.
Why Take This Board Governance Course?
Board members of Cyprus Investment Firms operate in an environment where corporate governance, conduct risk, financial resilience and digital operational resilience are increasingly interconnected. While general compliance rules apply across operations under our GRC & ESG Courses, executive leadership requires a consolidated view of cross-regulatory risks. A decision to enter a new market, introduce a product, accelerate digital client acquisition or rely on a critical technology provider can create multiple risks that require coordinated Board oversight. This programme helps directors move beyond passive receipt of management reports towards more effective challenge, informed decision-making and demonstrable re
Strengthen Corporate Governance & Board Accountability
Effective corporate governance depends on clearly defined responsibilities, independent oversight and the ability of directors to challenge management constructively. For interactive Board-level strategy and AI oversight discussions, consider our live Corporate Governance, ESG & Digital Risk Course for Boards (H1023).
The course helps participants understand:
- Collective Board accountability versus management execution
- Executive and non-executive director responsibilities
- Board committees, delegation and reserved matters
- Independence and reporting of Compliance, Risk, Internal Audit and the AMLCO
- Conflicts of interest and conduct culture
- Board minutes, action logs and governance evidence
Participants learn how to identify weaknesses in Board reporting, challenge management explanations and ensure that important decisions are properly documented.
Improve Board Oversight of Business Strategy & Risk Appetite
Business growth can create new exposures through revenue concentration, client acquisition, products, jurisdictions and external providers.
This section helps directors evaluate:
- Business-model sustainability and revenue dependence
- Product, client, jurisdiction and provider concentrations
- Risk appetite statements and measurable limits
- Key risk indicators and escalation thresholds
- Growth and market-entry proposals
- Conditions, constraints and evidence required for Board approval
The emphasis is on challenging strategic decisions before additional risk becomes embedded in the firm’s operations.
Strengthen Financial Resilience & Wind-Down Oversight
Boards need a clear understanding of whether their CIF has sufficient financial resources to withstand adverse developments and protect clients.
The programme explores:
- Capital and liquidity headroom
- Financial stress testing and adverse scenarios
- Operational losses and financial vulnerabilities
- Assumptions supporting management forecasts
- Wind-down triggers and operational feasibility
- Remediation decisions during financial stress
Participants develop a stronger understanding of the questions directors should ask when reviewing financial resilience and proposed mitigating actions.
Enhance MiFID II Conduct & Customer Protection Oversight
Customer outcomes are an essential element of effective governance for investment firms. To explore specific front-office conduct rules in depth, directors can review our Financial Regulation Courses directory.
The course examines how Boards can monitor:
- Product governance and target markets
- Suitability and appropriateness indicators
- Digital client journeys and distribution arrangements
- Affiliates, finfluencers and marketing promotions
- Costs, charges and execution outcomes
- Complaints, root causes and customer redress
- Client-money safeguarding and reconciliation exceptions
Directors learn how to distinguish isolated operational issues from patterns indicating potential weaknesses in conduct governance or client protection.
Strengthen AML/CFT, Sanctions & Financial Crime Governance
The Board must receive sufficient information to understand material financial-crime exposure and determine whether controls and remediation are effective.
Participants examine:
- Business-wide money laundering and terrorist financing risk assessments
- AMLCO reporting and escalation
- High-risk clients and jurisdictions
- Customer due diligence and enhanced due diligence backlogs
- Sanctions screening and escalation
- Fraud-risk indicators
- Market-abuse and market-integrity monitoring
- Remediation, assurance and closure evidence
The course maintains a Board-level perspective, focusing on oversight and accountability rather than operational compliance procedures.
Understand DORA & Digital Operational Resilience Responsibilities
The Digital Operational Resilience Act (DORA) makes ICT risk and resilience an important area of management-body accountability. If you are seeking complete self-paced technical implementation modules under DORA, visit our dedicated Digital Operational Resilience Courses section.
This programme helps directors challenge information on:
- ICT risk governance and Board responsibilities
- Critical business services and ICT risk tolerance
- ICT incidents and customer impact
- Escalation and incident communications
- Business continuity and recovery objectives
- Recovery testing and remediation
- Digital operational resilience reporting to the Board
The content is designed for financial-services directors rather than technical cybersecurity specialists.
Improve Oversight of ICT Outsourcing & Critical Third Parties
Investment firms increasingly depend on external technology, infrastructure and service providers.
The course examines:
- Critical ICT service-provider dependencies
- Outsourcing concentration risk
- Subcontracting chains and service locations
- Contractual controls and audit rights
- Registers of information and provider monitoring
- Exit strategies and substitutability
- Migration feasibility and operational contingency planning
Participants learn how to challenge provider resilience and understand why outsourcing does not eliminate retained Board accountability.
Develop Evidence-Based Board Decision-Making
Throughout the programme, participants practise assessing whether Board information is complete, consistent and sufficient for a defensible decision.
The course emphasises the governance evidence trail:
Information → Challenge → Decision → Action → Assurance → Closure
This approach helps directors translate regulatory expectations into more meaningful Board oversight and follow-up.
Learn at Your Own Pace
The course is delivered online through Moodle and Articulate Rise 360, enabling participants to learn at a time that suits their professional commitments. You can explore this and other flexible modules within our Financial Regulation Self-Paced Courses Category. Participants can pause and resume lessons, revisit complex concepts, complete interactive knowledge checks and use downloadable learner notes for future reference.
What Is Included
- Interactive Articulate Rise 360 training covering 10 Board-level lessons.
- Practical scenarios, management-information examples and decision-based knowledge checks.
- An integrated Board case examining several interconnected regulatory and operational risks.
- Downloadable learner notes.
- A 15-question final online assessment.
- Certificate of Completion following successful completion.
- Six months of online course access.
- Approximately four hours of structured professional learning (4 CPD).
Key Learning Objectives
By completing this 4 CPD self-paced course, participants will develop practical knowledge of the governance and oversight responsibilities of the Board of a Cyprus Investment Firm.
Distinguish collective Board accountability from management responsibilities and independent control-function reporting.
Learners will be able to:
- Evaluate governance structures and committee responsibilities.
- Understand delegation, reserved matters and accountability.
- Challenge the quality of Board reporting and management information.
- Identify conflicts of interest and weaknesses in governance arrangements.
- Recognise the importance of documented challenge, decisions and follow-up actions.
Assess whether growth proposals and strategic decisions are consistent with a firm’s risk appetite and operational capacity.
Learners will explore:
- Revenue and business-model concentrations.
- Product, jurisdiction, client and provider dependencies.
- Risk limits, early-warning indicators and escalation thresholds.
- Board scrutiny of business expansion proposals.
- Conditional approvals and risk mitigation requirements.
Understand how directors should oversee financial resilience without assuming operational finance responsibilities.
Learners will examine:
- Capital and liquidity adequacy from a Board perspective.
- Financial risk indicators and stress-testing scenarios.
- Management assumptions and mitigation plans.
- Wind-down triggers and client-protection considerations.
- Board decisions during financial or operational stress.
Strengthen oversight of conduct risk, product distribution and customer protection.
Learners will be able to:
- Challenge target-market and product-governance information.
- Evaluate suitability, appropriateness and execution-related indicators.
- Assess digital distribution and marketing risks.
- Monitor complaints, costs, charges and redress.
- Recognise warning signals in client-asset safeguarding and withdrawals.
Understand the Board’s role in monitoring the arrangements used to protect client money and assets.
Learners will examine:
- Safeguarding governance.
- Reconciliation exceptions and escalation.
- Withdrawal controls.
- Bank and custodian concentration.
- Contingency planning.
- Assurance and remediation evidence.
Understand how to evaluate financial-crime exposure through Board-level information and independent reporting.
Learners will explore:
- AML/CFT risk governance and the business-wide risk assessment.
- The AMLCO’s reporting and escalation responsibilities.
- High-risk exposures and due diligence backlogs.
- Sanctions screening and remediation.
- Fraud and market-integrity risk indicators.
- Financial-crime assurance and closure evidence.
Develop the ability to challenge ICT risk information and oversee operational resilience under DORA.
Learners will examine:
- Management-body accountability for ICT risk.
- Critical services and ICT risk tolerance.
- ICT incident reporting and escalation.
- Business continuity and recovery arrangements.
- Recovery testing and remediation.
- Board oversight of digital operational resilience.
Use realistic governance scenarios to identify missing information, challenge management assumptions and make defensible decisions.
Learners will practise:
- Prioritising material risks.
- Identifying incomplete or conflicting management information.
- Challenging management recommendations.
- Deciding whether to approve, constrain or escalate proposals.
- Assigning actions, deadlines and accountability.
- Determining the evidence required before issues can be closed.
Course Curriculum
Become familiar with the Moodle learning environment, course navigation, resources and completion requirements. Understand how to approach the interactive Board-level lessons and assessment.
Examine the distinction between Board and management responsibilities, collective accountability, delegation, reserved matters, Board committees and independent control functions. Explore governance culture, conflicts, Board packs, minutes and closure evidence.
Assess revenue models, risk concentrations, growth strategies and risk-appetite limits. Learn how to challenge market-entry proposals, management dashboards, breaches and adverse trends before approving material changes.
Explore Board oversight of capital, liquidity, stress testing and adverse scenarios. Challenge management assumptions, evaluate mitigating actions and consider wind-down triggers, client protection and financial-resilience decisions.
Review MiFID II product governance, target markets, suitability and appropriateness indicators, digital distribution, affiliates, promotional activity, costs, execution outcomes, complaints and systemic remediation.
Understand Board oversight of client-money and asset-safeguarding arrangements, reconciliation exceptions, withdrawal controls, bank and custodian concentration, contingency planning, assurance and remediation.
Examine AML/CFT governance, the business-wide ML/TF risk assessment, AMLCO reporting, high-risk exposure, due diligence backlogs, transaction-monitoring effectiveness, remediation and emerging EU AML developments.
Assess sanctions exposure, ownership and control, screening effectiveness, fraud indicators and market-abuse surveillance. Focus on Board-level escalation, assurance and evidence that material issues have been resolved.
Understand management-body accountability for digital operational resilience under DORA. Explore critical services, ICT risk tolerance, incidents, customer impact, business continuity, recovery objectives, testing and remediation.
Assess critical ICT providers, concentration, subcontracting chains, audit rights, contractual controls, registers of information, ongoing monitoring, substitutability and tested exit strategies.
Apply the learning to a fictional digital retail CIF facing rapid affiliate-led growth, complaints, overdue financial-crime files, financial pressure and a critical provider outage. Identify urgent risks, challenge conflicting data and set defensible Board actions.
Consolidate the learning with downloadable Board-level notes and complete the 15-question Moodle assessment. Successful completion of the required learning and assessment leads to a Certificate of Completion.
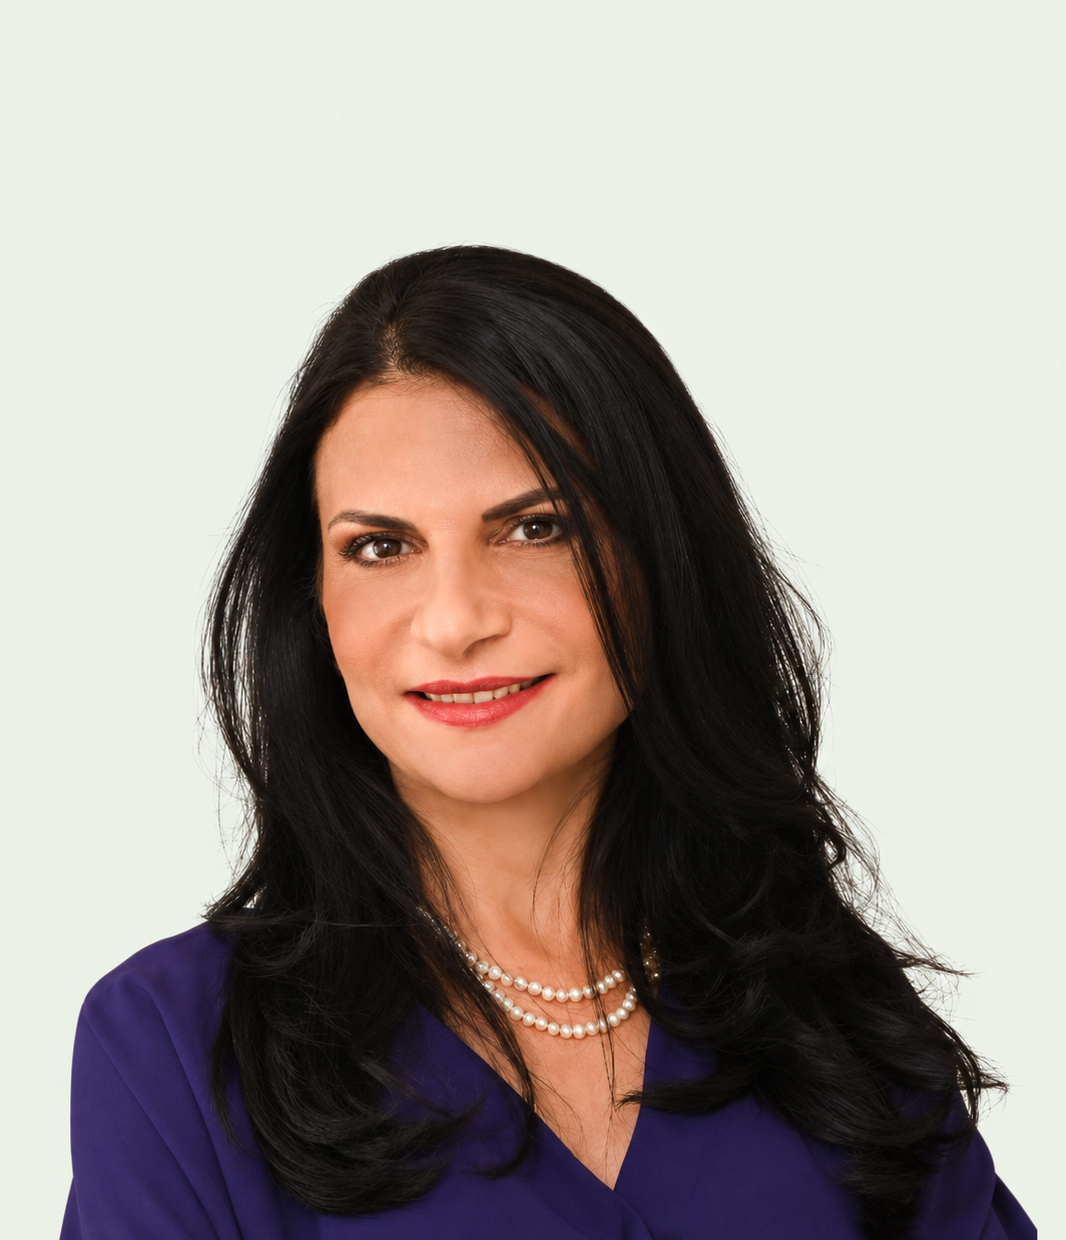
Meet the Trainer
Fees & Registration Details
FAQs – Frequently Asked Questions
This is a 4 CPD self-paced online course covering the practical governance and regulatory oversight responsibilities of directors and senior management of Cyprus Investment Firms. It examines corporate governance, risk appetite, financial resilience, MiFID II conduct, client-asset safeguarding, AML/CFT, sanctions, DORA, ICT incidents and third-party risk.
Board governance standards and management body responsibilities for CIFs are supervised by the Cyprus Securities and Exchange Commission (CySEC), which enforces compliance with European and national financial regulations.
Official regulatory standards regarding management body oversight for ICT risk under DORA are published by the European Securities and Markets Authority (ESMA) alongside joint European Supervisory Authority guidelines.
The programme is designed for executive and non-executive directors, Board committee members, CEOs, senior management, Compliance Officers, AMLCOs, Risk Managers, Internal Auditors, company secretaries and professionals preparing for senior governance roles in regulated financial services.
Yes. The course addresses corporate governance and management-body oversight relevant to Cyprus Investment Firms, including Board accountability, committee structures, independent control functions, risk management, escalation, documented decisions and evidence of effective oversight. Specific requirements must be considered in light of each firm’s regulatory circumstances.
Yes. The course examines management-body accountability for ICT risk and digital operational resilience under DORA. Topics include critical services, ICT risk tolerance, incidents, recovery arrangements, business continuity, critical third-party dependencies, subcontracting and exit planning. It is designed for Board oversight rather than technical cybersecurity operations.
No. The DORA content is management-body focused and does not require participants to perform cybersecurity tasks. It concentrates on the information directors should request, the questions they should ask and the evidence needed to oversee ICT risk, incidents and critical providers.
Participants work with Board-level risk indicators, financial and customer-outcome data, AMLCO reporting, safeguarding exceptions, ICT incidents and management dashboards. They practise identifying missing or conflicting information, testing assumptions, setting conditions and following actions through to closure.
Yes. The programme examines Board-level oversight of financial-crime risk assessments, AMLCO reporting, high-risk exposures, due diligence backlogs, monitoring effectiveness, sanctions screening, fraud indicators, market integrity and remediation evidence.
Yes. The course includes target-market governance, suitability and appropriateness indicators, digital client journeys, marketing and affiliate activity, costs, execution outcomes, complaints, client-money safeguarding and redress. The focus is on recognising customer-outcome risks and determining when Board intervention is needed.
Yes. The course is designed for an experienced professional audience but does not require non-executive directors to perform operational compliance functions. It explains how to challenge management, interpret key Board information and exercise oversight across specialist areas.
It examines growth and concentration risks, risk appetite, capital and liquidity headroom, stress testing, operational losses and wind-down planning. Participants learn how to challenge management assumptions and evaluate proposals from a Board perspective.
The programme provides 4 CPD credits and approximately four hours of structured Board-level learning. Participants complete the required learning and final assessment to receive a Certificate of Completion.
Participants receive six months of online access, allowing them to progress at their own pace and revisit the course content and learner notes during that period.
Yes. The course includes a 15-question online final assessment delivered through Moodle. A Certificate of Completion is issued following successful completion of the required learning and assessment.
The programme uses a fictional digital retail Cyprus Investment Firm to illustrate practical governance situations. The principles should be applied proportionately, considering each firm’s permissions, services, prudential classification, products, client-asset arrangements, jurisdictions and outsourcing dependencies.